
What MLPS 2.0 Is and Why It Matters for Foreign Companies
If you run an IT system in China—whether it is a customer database in Shanghai, a factory control network in Suzhou, or a cloud platform serving Chinese users—you are likely subject to China’s Multi-Level Protection Scheme, commonly known as MLPS 2.0 or 等保2.0. It is not a voluntary best-practice framework. It is a mandatory cybersecurity compliance regime backed by law.
MLPS 2.0 took effect on December 1, 2019, replacing the original MLPS framework that had been in place since 2007. The update expanded the scope from traditional information systems to cloud computing, mobile internet, Internet of Things, industrial control systems, and big data platforms. For foreign companies, the practical implication is simple: more systems now fall under the rules, and the assessment requirements are more detailed.
The scheme is administered by the Ministry of Public Security (MPS) and implemented through local public security bureaus. It sits alongside other Chinese cybersecurity laws, including the Cybersecurity Law (2017), the Data Security Law (2021), and the Personal Information Protection Law (2021). MLPS 2.0 is the operational layer that determines how a company’s systems are graded, secured, tested, and supervised.
The Five Protection Levels and What They Mean
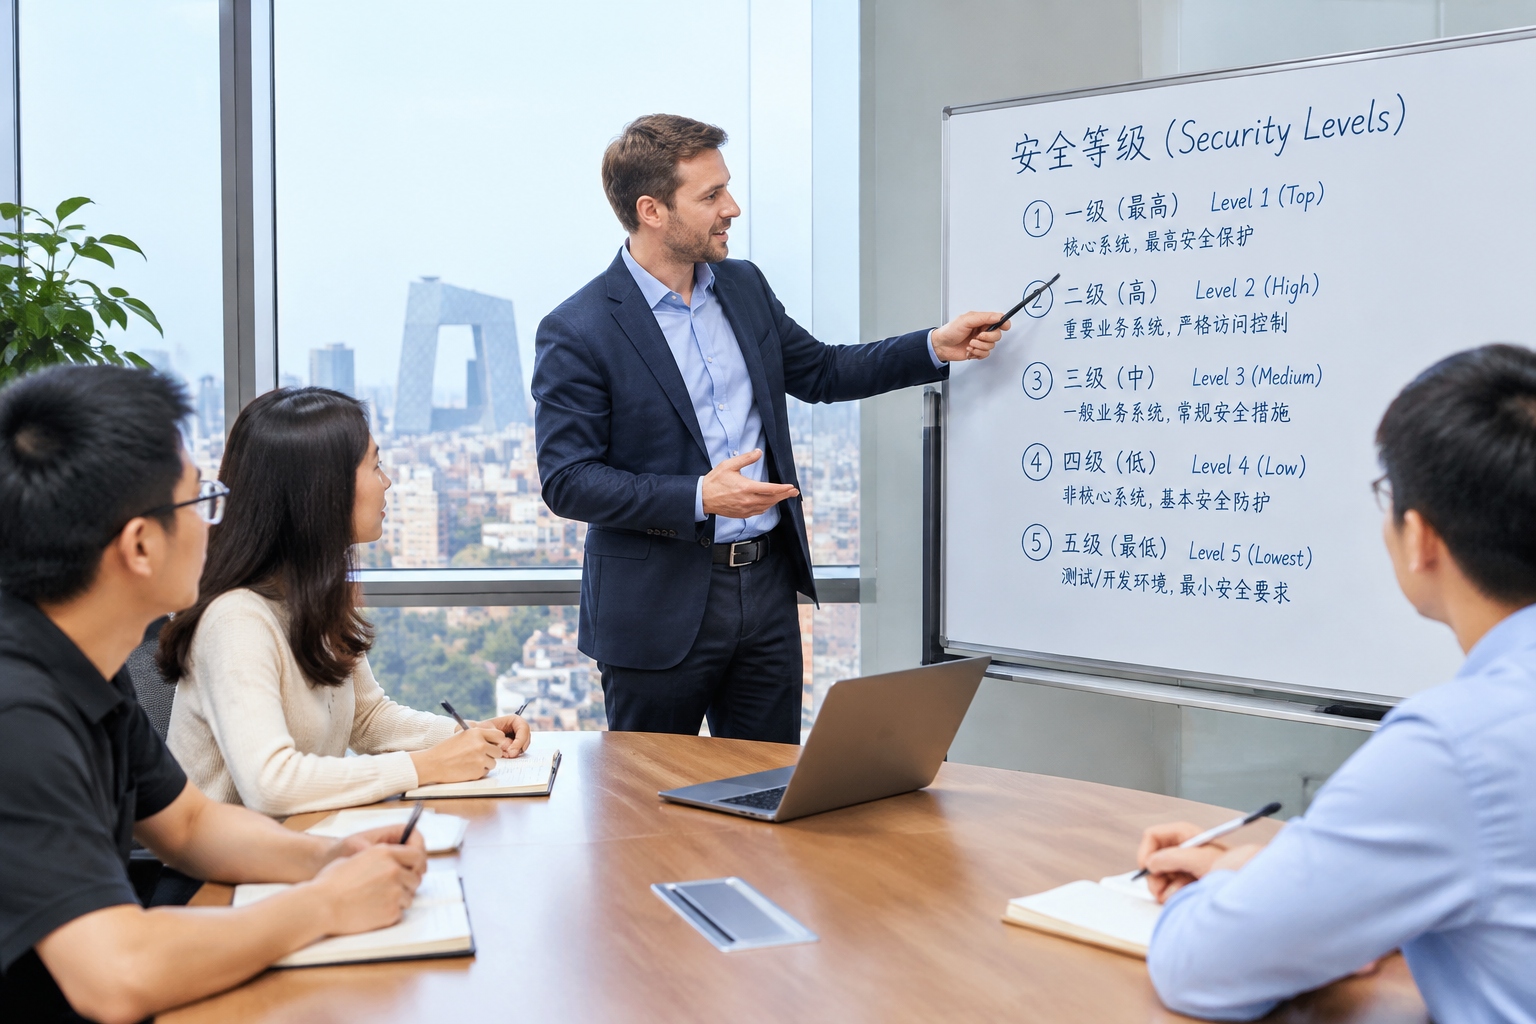
MLPS 2.0 classifies systems into five levels based on how much damage a security breach would cause to national security, public interest, or individual rights. The higher the level, the stricter the requirements.
Level 1: General Systems
These are systems whose compromise would cause limited harm to individual rights or general interests. They do not require mandatory third-party assessment or filing in most cases. Examples might include a small internal scheduling tool with no sensitive data.
Level 2: Important Systems
A breach would cause serious harm to individual rights or general interests, or minor harm to public order. Most foreign companies’ customer-facing systems, HR databases, and internal business platforms fall here. Level 2 systems must be graded, filed with the local public security bureau, and undergo regular assessment—typically every two years.
Level 3: Critical Systems
A breach would cause serious harm to public order or minor harm to national security. This level covers systems in finance, healthcare, energy, transportation, and large-scale consumer platforms. Level 3 requires annual assessment, stronger encryption, intrusion detection, and stricter access controls. Many foreign companies with significant Chinese user data or critical business operations will find their systems graded at Level 3.
Level 4: Highly Critical Systems
A breach would cause particularly serious harm to public order or serious harm to national security. These systems are typically found in core infrastructure, national defense, and major financial clearing networks. Level 4 requires mandatory annual assessment, real-time monitoring, and often physical isolation of critical components.
Level 5: Extreme Risk Systems
A breach would cause extremely serious harm to national security. This level is reserved for the most sensitive military and state security systems. In practice, foreign companies rarely encounter Level 5.
For most foreign businesses, the relevant question is whether their system is Level 2 or Level 3. That distinction determines cost, timeline, and ongoing compliance burden.
How to Grade a Foreign Company’s IT System: Level 2 or Level 3?
Grading is not self-declared without review. The company proposes a level, but the local public security bureau and, for Level 3 and above, industry regulators must approve it. Several factors push a system toward Level 3:
- User scale: Systems with more than 1 million registered users, or more than 100,000 daily active users, are often considered Level 3 candidates.
- Data sensitivity: Systems processing personal biometric data, financial records, health information, or large volumes of personal data are more likely to be Level 3.
- Business criticality: If the system supports essential services such as payment, logistics, or public communications, it may be graded Level 3.
- Industry rules: Finance, healthcare, education, and telecom regulators often issue their own grading guidance that pushes systems to Level 3.
- Cross-border data flows: Systems that transfer data outside China face additional scrutiny and are more likely to be graded at a higher level.
A practical example: a French design firm in Shanghai with a 30-person office and a local CRM system holding client contact details would likely be Level 2. A German automotive supplier with a connected car platform serving 500,000 Chinese users would almost certainly be Level 3.
The MLPS Assessment Process: Grading, Filing, Remediation, Testing, and Supervision
The process has five main stages. Each stage has specific deliverables and timelines.
Step 1: Grading (定级)
The company conducts a self-assessment to propose a protection level. This involves documenting the system’s purpose, data types, user numbers, and potential impact of a breach. The grading proposal is then submitted to the local public security bureau. For Level 3 and above, an industry expert review is typically required.
Step 2: Filing (备案)
Once the grade is approved, the company files the system with the local public security bureau. Filing typically requires: the grading report, network topology diagram, security protection plan, and company registration documents. The bureau issues a filing certificate. This step is mandatory for Level 2 and above. Without filing, the company cannot legally operate the system.
Step 3: Security Construction and Remediation (安全建设整改)
The company must implement security measures required for its level. For Level 2, this includes access control, audit logs, malware protection, and data backup. For Level 3, additional requirements include encrypted transmission, intrusion detection, security auditing, and regular vulnerability scanning. Many foreign companies hire local cybersecurity vendors to perform a gap analysis and remediation.
Step 4: Assessment (测评)
An authorized testing organization—licensed by the Ministry of Public Security—conducts an on-site assessment. The assessment covers physical security, network security, host security, application security, data security, and management processes. Level 2 systems are assessed every two years; Level 3 systems annually. The assessment produces a report that must be filed with the public security bureau.
Step 5: Supervision (监督检查)
Public security bureaus conduct periodic inspections. They may review assessment reports, check remediation progress, and test system defenses. For Level 3 systems, inspections are more frequent and may include penetration testing. Companies must maintain records of all security activities and be ready to demonstrate compliance at any time.
Legal Consequences of Non-Compliance
Failing to complete MLPS 2.0 requirements can lead to serious penalties under the Cybersecurity Law and related regulations.
- Warnings and fines: For first-time minor violations, the public security bureau may issue a warning and order correction within a deadline. Fines for companies can range from RMB 10,000 to RMB 100,000. For serious violations, fines can reach RMB 1 million.
- Personal liability: Responsible individuals—such as IT managers or legal representatives—can face personal fines of RMB 10,000 to RMB 100,000.
- Business disruption: Authorities can order suspension of operations, shutdown of the system, or revocation of business licenses in extreme cases.
- Reputation damage: Non-compliance can affect relationships with Chinese partners, customers, and regulators. It may also trigger additional scrutiny from other agencies.
- Cross-border implications: For foreign companies, non-compliance can complicate data export approvals and may be considered in broader corporate compliance reviews.
Enforcement has become more active since 2021. Public security bureaus in major cities like Beijing, Shanghai, and Shenzhen have conducted high-profile inspections of financial, healthcare, and e-commerce platforms. Foreign companies are not exempt.
What Foreign Companies Should Do Next
Start with a clear inventory of your IT systems in China. Determine which systems process personal data, serve Chinese users, or support critical business functions. Then assess whether each system is likely Level 2 or Level 3. If you are unsure, engage a local cybersecurity consultant who understands MLPS 2.0 and has experience with foreign companies.
Do not treat MLPS 2.0 as a one-time project. It requires ongoing documentation, annual or biennial assessments, and a willingness to adapt as regulations evolve. The companies that manage it well are those that integrate it into their regular IT governance, rather than treating it as a last-minute compliance scramble.
Start the discussion at forum.chinacomes.com