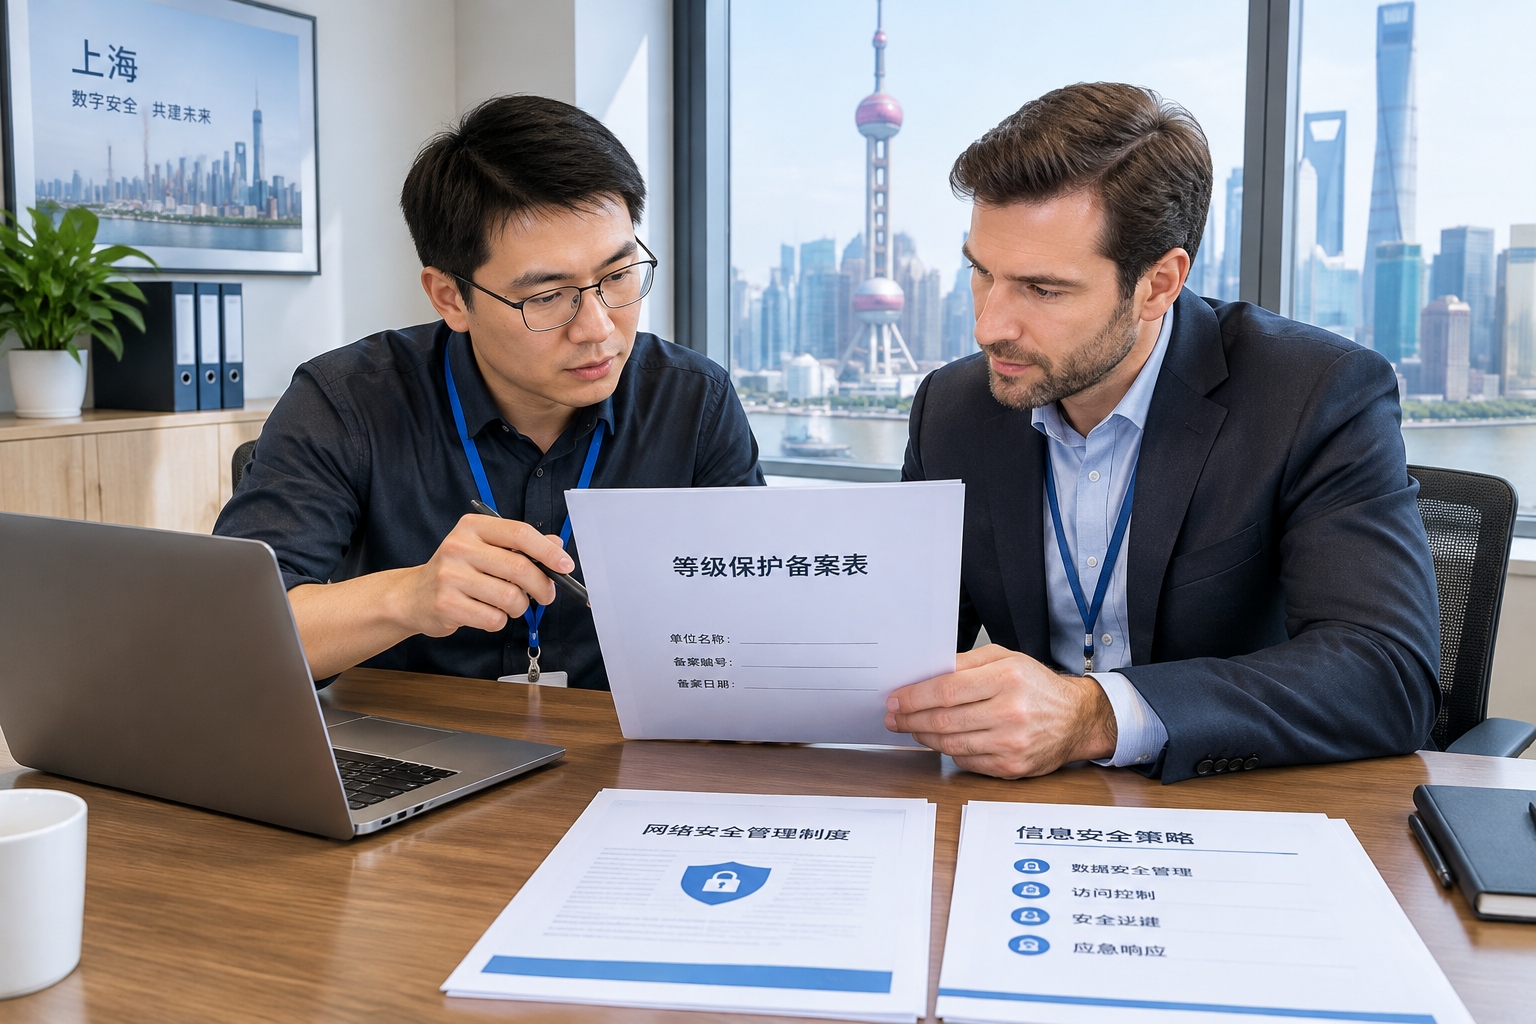

Omar, an IT director at a Stuttgart-controlled automation company near Suzhou, received a call in late November from the local public security bureau. “Your industrial software platform needs to complete a Multi-Level Protection Scheme filing,” the voice said. Omar had spent years protecting machines from hackers, but now he had to protect his company from paperwork. His first question: what exactly does a German company need to do with a Chinese cyber security law?
What Is MLPS 2.0 and Who Must Comply?
MLPS stands for Multi-Level Protection Scheme, usually called dengbao (等保) in China. The current version, MLPS 2.0, is based on the Cybersecurity Law of the People’s Republic of China, which has been effective since 2017. The technical baseline for MLPS 2.0 is the national standard GB/T 22239-2019. Think of it as a mandatory security audit that applies not only to Chinese state-owned enterprises but also to any network operator “that has a real impact on social order and public interest.” In practice, that includes almost every foreign-owned company supporting a business system online in China: email servers, ERP systems, factory automation connected to the internet, e-commerce websites, mobile apps handling customer data, and even internal office networks that store personal information of staff.
We’ve walked foreign companies through this process more times than I can count. The first scary step is always classification, but it is quieter than it sounds. Here’s the playbook.
Step 1: Determine Your System’s Protection Level
The level determines how much security you need and how often you must be assessed. China uses five levels, with Level 1 h ypothetical for small stand-alone systems and Level 5 reserved for rare, nation-critical systems. Most foreign companies end up at Level 2 or Level 3.
- Level 2: Systems where a failure would cause serious damage to citizens’ rights or social order, but not overwhelmingly so. Example: an internal HR or CRM system of a mid-sized manufacturing firm.
- Level 3: Systems that, if disrupted, would cause severe damage to public security and social order, or affect very large amounts of personal information. Example: a financial services platform, a regional logistics control center, or a healthcare network that stores patient health data.
Many foreign-funded technology companies assume they are automatically Level 3 because they process “important data.” In reality, the default classification for most corporate IT systems is Level 2 unless the regulator pushes you higher. The classification is not a self-service activity, though. You must prove your choice with a written assessment explaining how you evaluated the impact. And in some sectors, like finance or transportation, regulators have prescriptive tables that tell you exactly which level you fall into.
If you are not sure, get the evaluator in the room early. Most qualified third-party assessment centres, especially in Shanghai, Beijing and Shenzhen, offer a consultation to help you frame the classification. Don’t let pride (or fear) push you into an unnecessarily high level, but also don’t underestimate your exposure. A wrong classification that triggers a later penalty will cost more than the hours you save.
Step 2: Submit Your Filing Before a Deadline
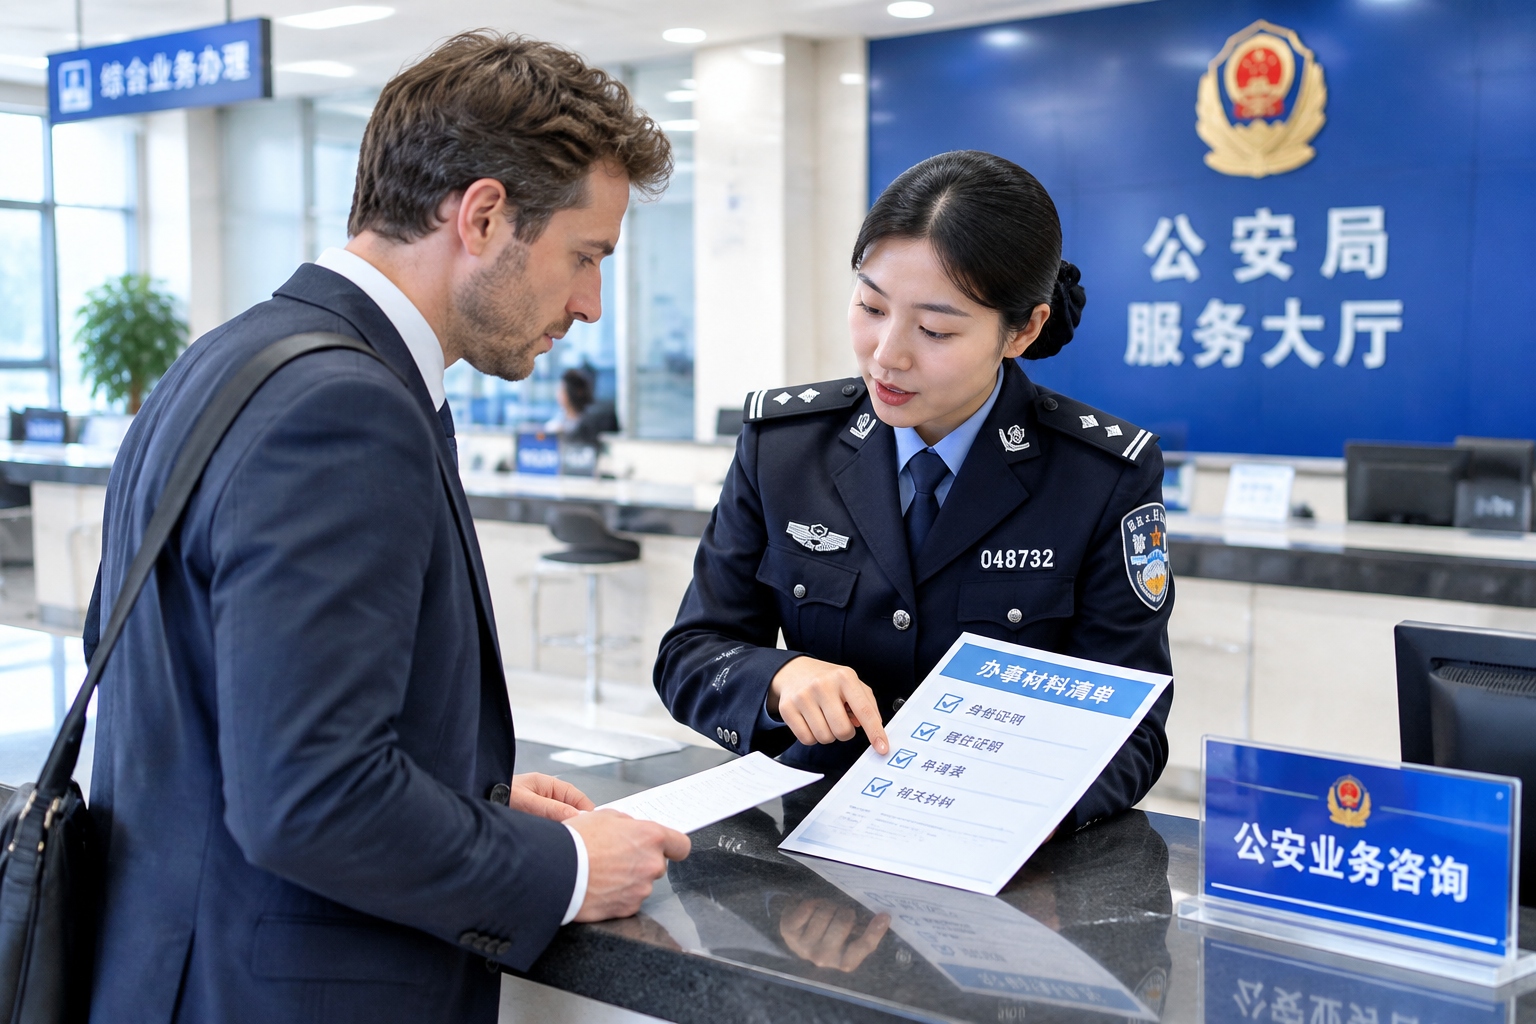
Once you have your level, you file with the local municipal public security bureau (PSB). The filing process is formally called dengbao beian (等级保护备案). Work out your filing package with enough time to fix missing items before the deadline. In many cities, you are expected to submit within 30 days after the system goes into operation. If you are discovering MLPS in the middle of a system’s life, the clock is already ticking, but PSBs often accept a late filing with a reasonable justification. Don’t wait another month.
- The official registration form (security protection level filing form).
- A concise system description: what it does, where it resides, which regulators oversee your business.
- The security evaluation report you generated during the level-determination process (it does not have to be a full technical assessment; often a written analysis is enough).
- A copy of your business license and the legal entity’s ID.
Do not expect the hall to be friendly at first glance. Public security officers are not cybersecurity consultants; they are there to check paperwork and give you an official registration number. If your paperwork is incomplete, they will give you a list of missing items on a yellow note. You fix it and come back. It is a normal step, not a warning.
Step 3: Arrange a Third-Party Assessment and Prepare for the Test
For Level 2 systems, the law does not strictly require an external test every year, but many foreign companies opt to do one anyway because the internal assessment burden is hard to maintain. For Level 3 systems, the rule is clear: you must undergo an assessment by a registered MLPS evaluation agency at least once a year. The assessment centre will look at roughly 80 controls across technical and managerial domains.
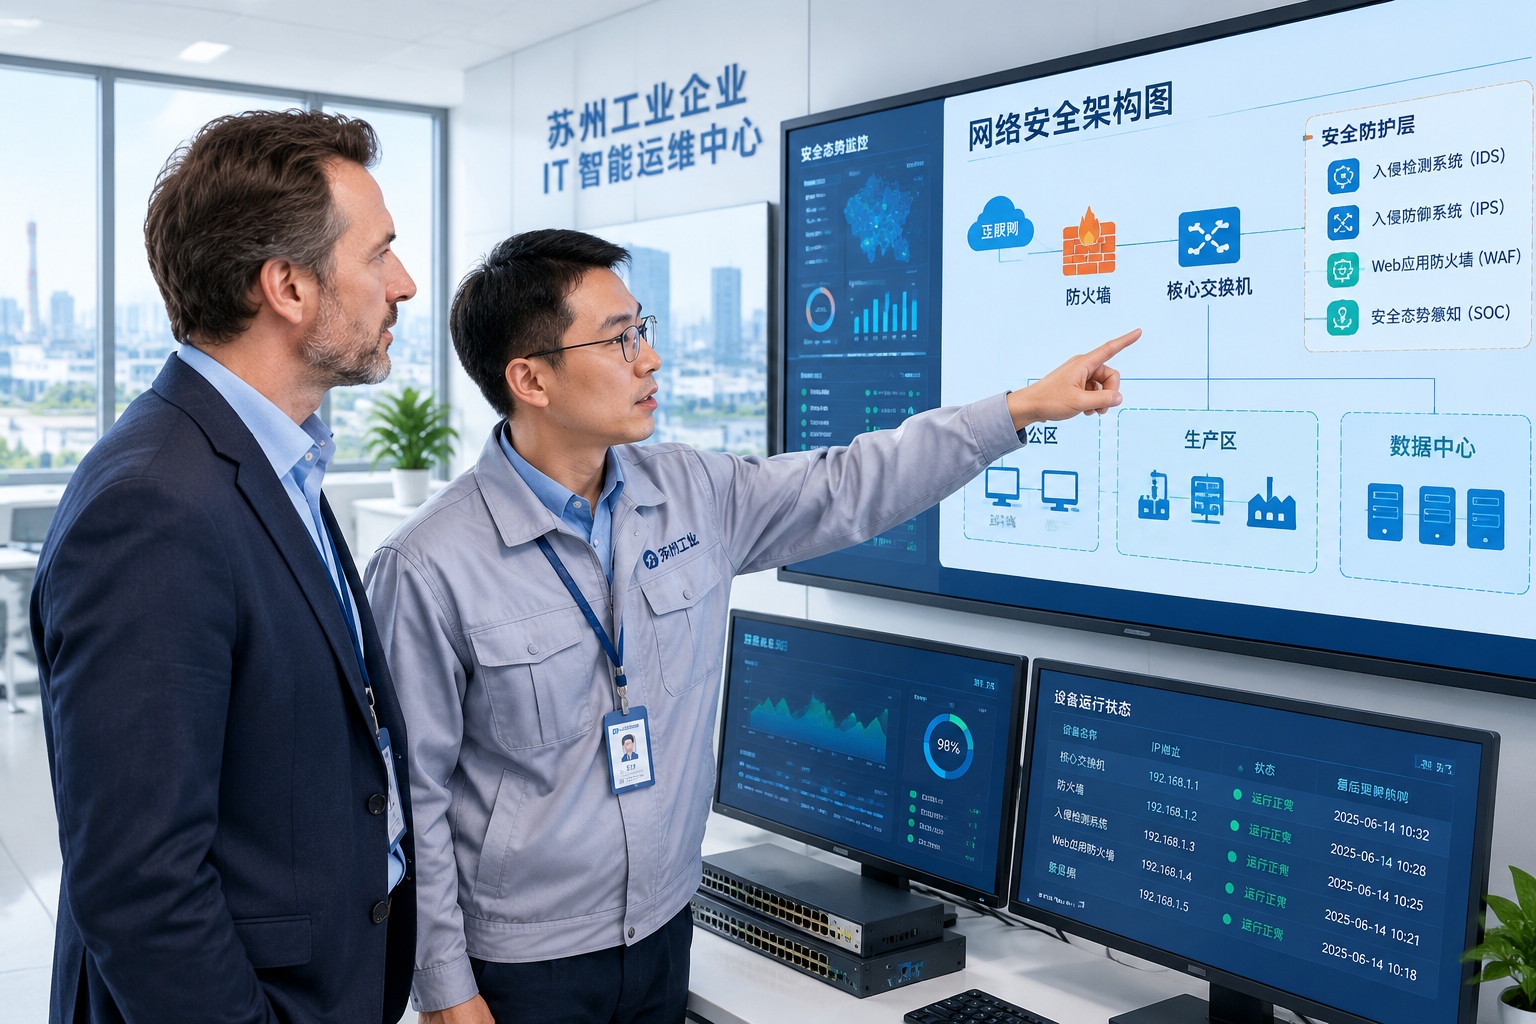
- Technical: access control, data encryption, network segmentation, intrusion detection, backup and recovery.
- Management: security policies, employee training, contingency plans, procurement security, outsourced development.
The assessment is not a one-day walkthrough. Expect it to take between two and four weeks from document review to on-site inspections. Some centres are backlogged in Q3 and Q4, so schedule early.
Here is a practical tip: many foreign companies have already built policies equivalent to ISO 27001 or NIST, but they fail MLPS because the Chinese control numbers do not match their own documentation. The assessment team usually does not want to see your fifteen appendices of internal wiki pages; they want a one-to-one correspondence between each MLPS requirement and the evidence you present. Create a mapping table before the formal assessment starts. You do not need to rewrite your security policy, but you will need to translate and re-index it into the MLPS framework.
Step 4: Remediation: Most Companies Need to Fix Something
Once the assessor sends you the pre-assessment findings, you will likely see a list of medium and high risk items. Common gaps for foreign companies include:
- Encrypted communication not enabled for internal services (because your global policy assumes an internal network is safe).
- Log storage shorter than the six-month minimum required for Level 3.
- No Chinese-language incident response plan that clearly designates a local security officer.
- Access from overseas staff with no multi-factor authentication.
Remediation does not always mean buying new expensive firewalls. Often it means changing a configuration, enabling encryption, or drafting a missing procedure. In my experience, roughly 70% of the gaps can be closed with documentation and configuration changes. The rest are technical fixes that might involve a vendor invoice or two.
The time needed for a typical remediation phase is about 30 to 60 days. If you are on a tight timeline, ask the assessment centre to reprioritise the highest risk findings first. You will still need to fix all “high risk” findings before the final report can show a “pass”, but medium risk items can sometimes be planned with a future date in your continuous improvement plan.
After remediation, the evaluator may visit again to verify the fixes, or in light cases, accept your written evidence on a shared drive. Do not exaggerate. Assessment centres are accountable for the accuracy of the final report, and the public security bureau can audit the centre’s work at any time.
Step 5: If You Fail the Assessment: Next Steps and Bigger Risks
MLPS is not a pass/fail exam in the way we think of a school test. The evaluator writes a conclusion that includes an overall rating, but a negative conclusion can appear in many forms:
- Two or more high-risk items remain, and the evaluator refuses to issue a compliant report.
- The evaluator issues a report with “major non-conformities” documented.
- The evaluator reports to the public security bureau for suspected illegal activity.
If you receive a non-compliant conclusion, you are given a rectification deadline by the regulator. The length varies from 30 to 90 days depending on the severity and the individual PSB office. During this period, you are expected to close the gaps and show a new version of the evidence. If you still fail after that, the escalation is real: the Cybersecurity Law allows the competent authority to order rectification, give a warning, impose fines ranging from RMB 10,000 to 100,000, and in serious cases, issue a penalty from RMB 100,000 to 1,000,000 to the responsible person directly in charge. Reviews of non-compliance actions against foreign-companies tend to be publicised locally; for a foreign-invested entity, that publicity can hurt less than the fines.
One nuance: an MLPS failure is not the same as a data breach notification. Failing the assessment is a compliance violation; suffering a breach might trigger separate data privacy laws such as the PIPL (Personal Information Protection Law). But the two are often linked in investigation reports, and a history of MLPS non-compliance makes it easier for the regulator to impose a stricter penalty under PIPL.
Final Tips from the Trenches
Start MLPS work before a customer, partner or regulator forces you to. Treat it as a business continuity issue because it needs operational evidence from your whole IT team. Keep one person responsible for coordinating with the assessment agency; typically this is the information security manager or IT director.
If you have multiple systems, consider grouping systems with the same business risk into one MLPS “system” for assessment, as long as they share the same network boundary and operators. This drastically reduces the cost and paperwork.
The good news is that MLPS 2.0 is not a checklist to scare foreign investors. It is a management and technical baseline that can improve your cybersecurity posture—and it can also be part of a solid conversation with your board about how seriously you take local legal obligations. The sooner you start, the less annoying the yellow note becomes.
Start the discussion at forum.chinacomes.com