

Anna, a compliance officer for a German software firm in Shanghai, has spent the past three months doing something her job never required before: mapping every piece of customer data that flows from China to the company’s Frankfurt headquarters. Her firm is not Chinese, and most of its clients are not Chinese either. But under China’s Personal Information Protection Law, or PIPL, that fact no longer shields her company from local rules.
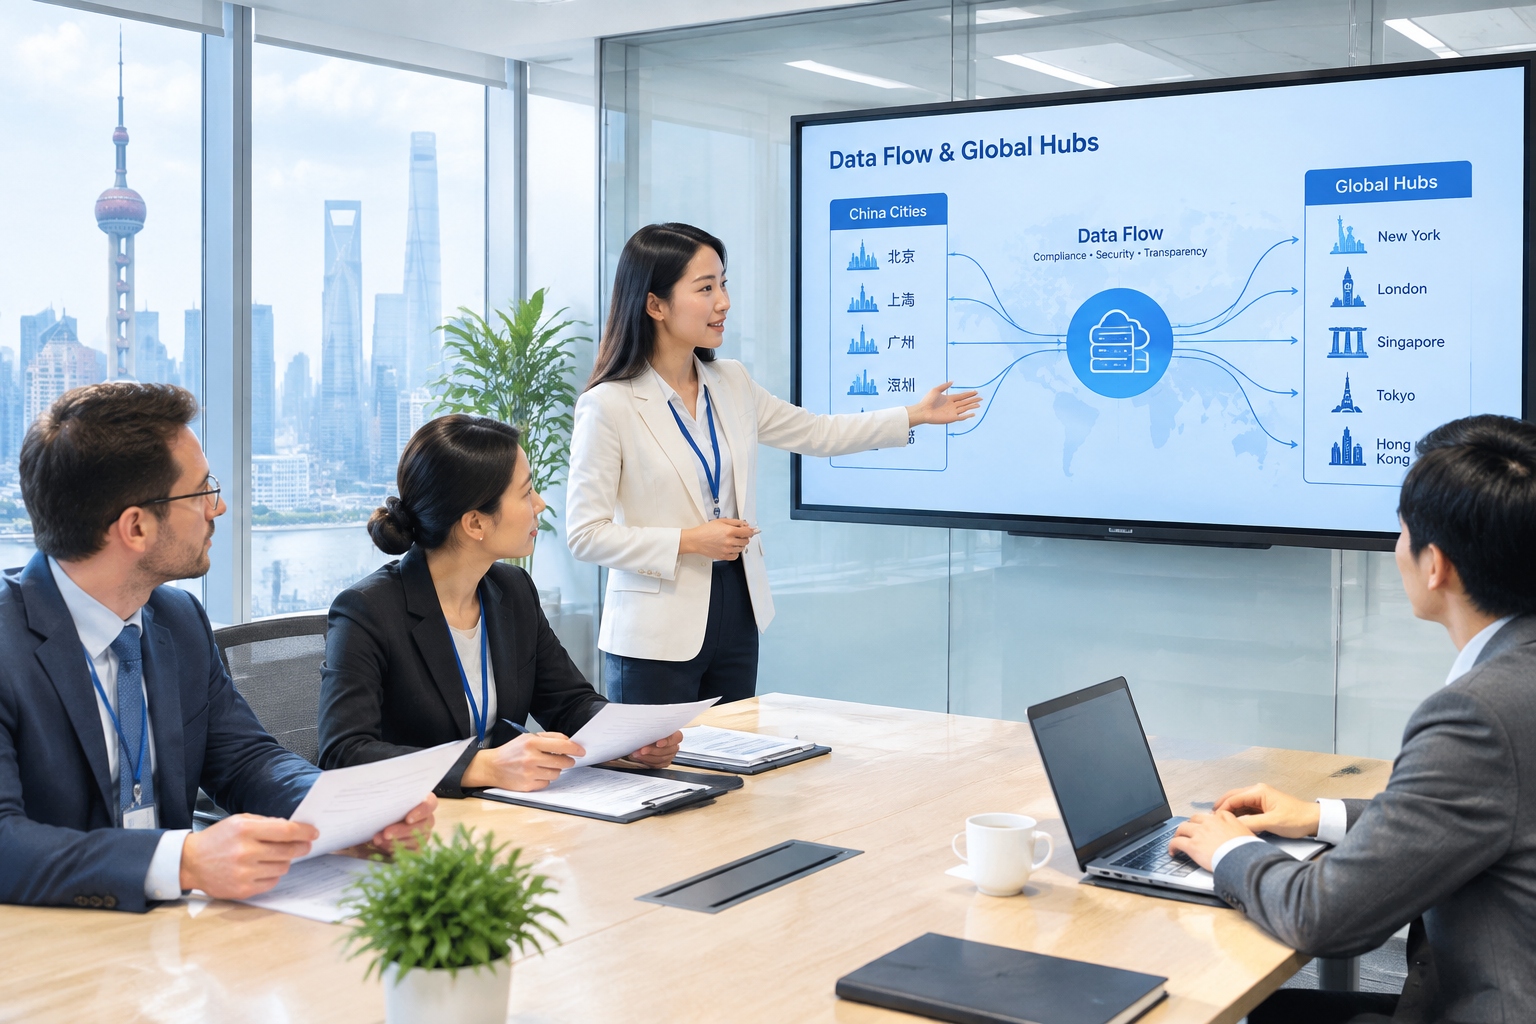
PIPL took effect on November 1, 2021. It is China’s first comprehensive law devoted to personal information protection, and it borrows several concepts from the European Union’s GDPR — but with notable differences. For any foreign company with customers, employees, suppliers or business partners in China, knowing how PIPL applies is now a basic condition for doing business here.
Who Needs To Comply With PIPL?
PIPL has a wide reach. It applies first to all organisations that process personal information inside China, whether the company is Chinese, foreign or a joint venture. It also applies to organisations outside China that process the personal information of people in China in order to provide products or services to them, or to analyse and evaluate their behaviour. If your website accepts orders from Shanghai or your app tracks location data from Chinese users, you are caught by this second rule.
The law defines personal information as any information that can identify a person individually, alone or when combined with other information. That includes a name, a mobile phone number, an email address, a location, even the behavioural profile built on a browsing history.
Overseas processors have an additional duty. PIPL Article 53 requires them to set up a dedicated department or appoint a representative in China to handle privacy matters. This representative can be a person or an agency that the regulator can contact. For a company based in Munich or Chicago, this is often one of the first steps to put in place.
Getting User Consent Right
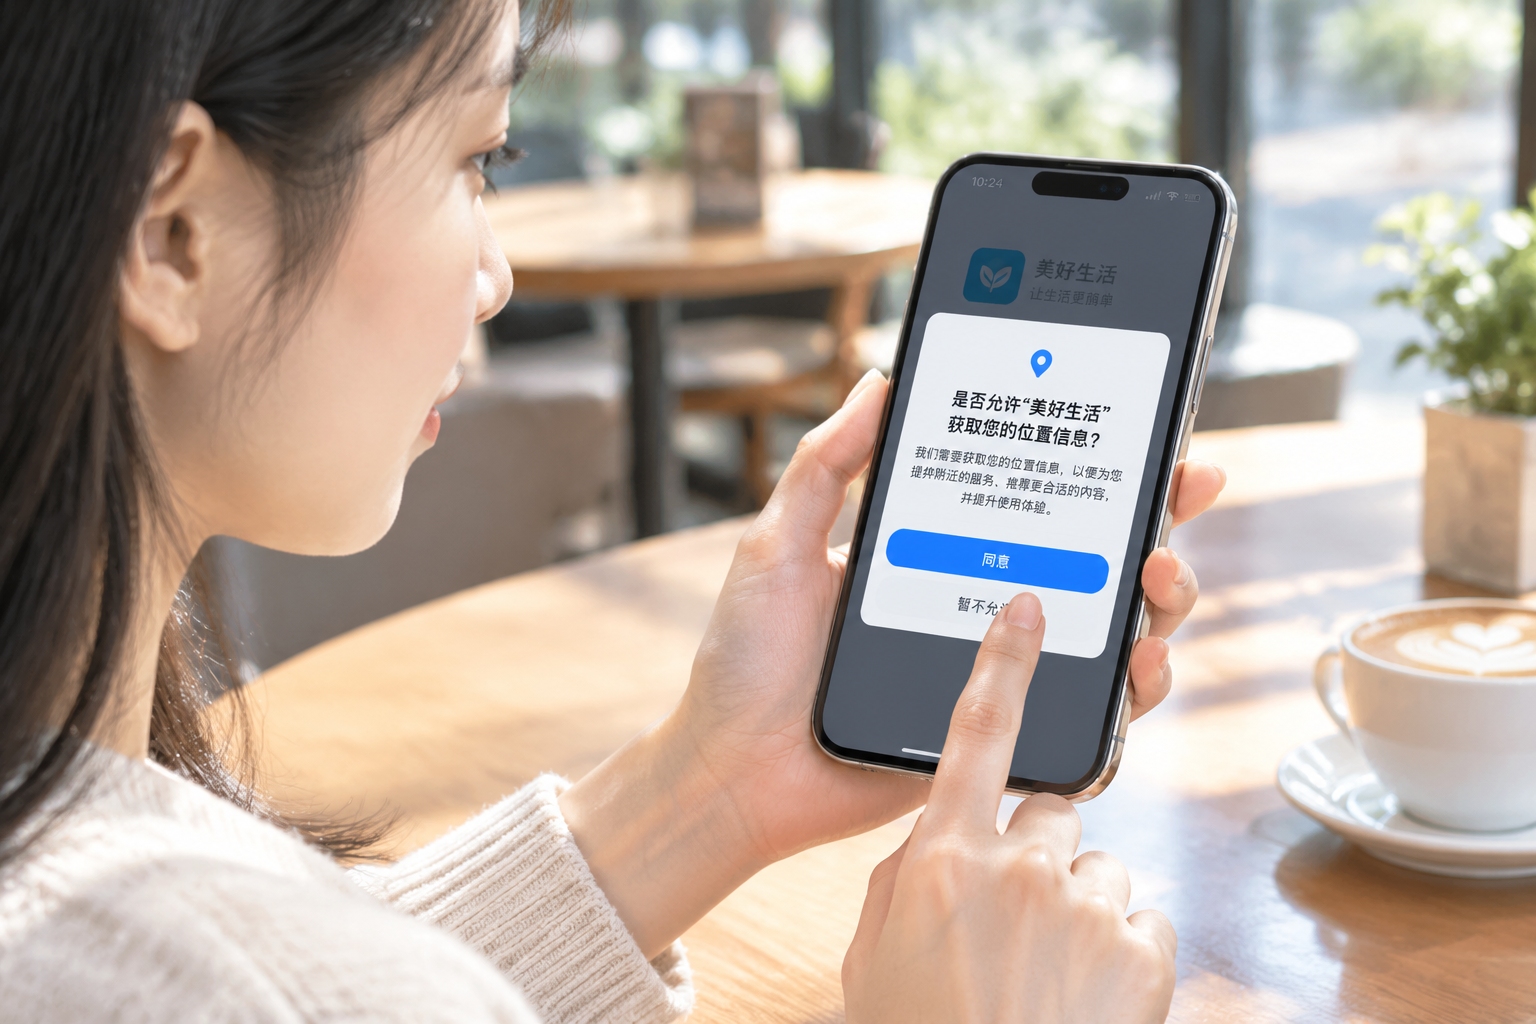
The most visible change for users is the way PIPL handles consent. Under the law, consent must be “informed, voluntary and unambiguous”. More importantly, for certain processing activities, companies must obtain “separate consent” – a single, dedicated permission that cannot be buried in the general terms and conditions.
Separate consent is required in several cases: transferring personal information to a third party, using it for a purpose other than the one originally stated, handling sensitive personal information, and sending personal information overseas. For example, if a fitness brand operating in Shanghai wants to share its customers’ workout histories with an overseas marketing platform, it cannot just tick a box in its privacy policy. It needs to explain exactly what is being shared, with whom and why, and then ask for an explicit yes or no.
Sensitive personal information gets extra treatment. That includes biometric data, health records, financial account details, precise location, religion and information about children under 14. Collecting and processing this kind of data requires a separate, specific consent. The law also says you must inform people of the purpose and the way you process such data, and you need their independent choice.
What does this mean for an app or a website? The classic “I have read and agree to the terms” checkbox is no longer enough. You have to design pop-up windows that make the choices clear, provide a way to withdraw consent as easily as it was given, and never make “no” a punishment – a user who refuses consent still has the right to use the core service unless the data is strictly necessary.
Data Localization: When Does Data Have To Stay In China?
One of the most debated parts of PIPL is localisation. Article 40 says that critical information infrastructure operators – CIIOs – and personal-information processors that reach a volume threshold determined by the Cyberspace Administration of China (CAC) must store personal information collected in China inside Chinese territory. When such data needs to go overseas, the company must pass a security assessment first.
CIIO is a separate concept under the Cybersecurity Law. It covers organisations in sectors such as telecommunications, energy, transportation, water supply and financial services, if their operations could hold a major impact on national security and public interest if disrupted. Foreign companies in these sectors are likely to be designated as CIIOs when they run critical facilities in China.
For most foreign firms outside those industries, the localisation requirement does not automatically apply. However, if they handle “important data” – state secrets and data that could be linked to national security – the rule tightens again. The practical message is: you cannot simply assume your data is outside the localisation requirement. The first step is to check whether your company or one of your Chinese subsidiaries has been designated as a CIIO or handles important data. If the answer is yes, data storage has to be local.
Three Legal Paths for Cross-Border Data Transfers
Even when localisation does not apply, PIPL imposes heavy conditions on sending personal information abroad. Companies that need to transfer data out of China have three possible routes. All of them require a privacy impact assessment in advance, and none of them removes the need for separate user consent where it applies.
1. Security assessment by the CAC
This is the most demanding path. Under the Measures for Data Exit Security Assessment, a filing with the CAC is required for CIIOs, for processors that handle the personal information of more than 1 million people, and for processors that have cumulatively exported personal information of more than 100,000 people – or sensitive personal information of more than 10,000 people – since January 1 of the previous year. Foreign companies that are not CIIOs may still be pushed into this path if they run a large user base in China.
The security assessment can take months and the outcome is not guaranteed. It is not a one-off: the assessment needs to be repeated when the data transfer changes in scale or purpose, or when the contract between the parties changes.
2. Standard contractual clauses
The more common route for smaller exporters is the Standard Contract for the Export of Personal Information, issued by the CAC in 2023. It allows a company to export data without undergoing a security assessment if it is not a CIIO and if the volumes stay below the thresholds described above.
The standard contract sets out the rights and obligations of both parties – the data exporter and the overseas recipient – including responsibilities for breaches, data subject rights and whether to follow Chinese law or the law of the importing country. After both parties sign, the exporter files the contract with the local provincial cyberspace administration within 10 working days along with the privacy impact assessment. This route is not automatic: the regulator can reject the filing if the contract fails to meet requirements.
3. Certification by a professional body
The third route is certification. PIPL authorises independent professional bodies to certify companies that meet data-protection standards. For multinational groups that want to set up internal transfer mechanisms across their own entities, certification may be a better fit than a government assessment. China has published certification standards that are compatible with the GDPR concept of binding corporate rules. However, the certification mechanism is relatively new and accredited bodies are only now emerging, so it is not yet the default option.
Penalties and Real-World Risks
PIPL carries serious penalties. The maximum fine is 50 million yuan (roughly $7 million) or 5% of the violator’s previous year’s global revenue, whichever is higher – a figure close to GDPR’s maximal penalty. Individuals who are directly responsible can face fines between 10,000 and 1 million yuan and a lifetime ban from taking up data-protection management roles.
Regulators can also order a company to suspend operations until corrective measures are taken. Since the law’s enactment, many multinational companies have been watching enforcement cases against local tech firms, like the ride-hailing app DiDi in 2022, which was fined $1.2 billion for multiple violations of cybersecurity, data protection and personal information laws, including cross-border transfer issues. Although the exact breakdown of penalties is not fully public, that case made it clear that Chinese regulators are prepared to use the maximum levers.
Beyond government fines, there is also civil risk. Article 69 gives individuals the right to sue for damages caused by illegal processing. A concentrated group of consumers can also file a public-interest lawsuit. For foreign brands, litigation can cause reputation damage that is more expensive than any fine.
What Should Your Company Do Now?
Compliance starts with a data map. Identify where personal information comes from, where it is stored, who can access it, and whether any of it is leaving China. Then decide whether your company qualifies as a CIIO or crosses the CAC’s thresholds. If you are unsure, conservative planning is safer.
Next, prepare a set of PIPL-ready notices. Make sure your privacy policy explains what data you collect, why and how long you will keep it. Build a mechanism to collect separate consent for every trigger – sharing, transfer overseas, sensitive data.
If you fall under the standard contract path, sign the CAC’s model contract with your overseas processor and make the filing. If you are larger, start the security assessment well in advance. And always have a local representative who can answer regulator and user questions.
PIPL is not meant to stop international business; it is meant to make it more transparent. The companies that treat it as a genuine privacy discipline instead of a bureaucratic hurdle will find the process manageable.
Anna’s company eventually chose the standard contract route and hired a local data protection officer. It took two months of work, but now she can quickly answer any regulator’s question. That, in the end, is what compliance should give you: confidence.
Start the discussion at forum.chinacomes.com