

A compliance manager’s first morning with the law
When Sophia, a data compliance manager at a German-owned auto parts manufacturer in Suzhou, first opened an official translation of China’s Data Security Law (DSL), she was looking for a simple answer. Her factory stores vehicle test data, supplier information, and employee records. Is any of this classified as ‘important data’? If so, what must her company file with the authorities?
The law, which took effect on September 1, 2021, does not come with a checklist. Instead, it creates a layered system where many specific rules are delegated to industry regulators. That ambiguity can be unsettling for foreign investors. This article explains what the classification levels mean, how a foreign-owned enterprise can identify its compliance duties, and what happens if a company misses a step.
Why China put data security into its own statute
The DSL is China’s first comprehensive data security law. Together with the Cybersecurity Law (2017) and the Personal Information Protection Law (2021), it forms the basic legal framework for data governance in China. The DSL applies to any organisation that collects, stores, uses, processes or transmits data in mainland China, including wholly foreign-owned subsidiaries. It also has extraterritorial effect: if a foreign organisation processes Chinese data overseas and harms the security or interests of Chinese citizens or the state, Chinese authorities may investigate.
Beijing’s stated purpose in Article 1 is threefold: ensure data security, protect the lawful rights of citizens and organisations, and promote the healthy development of the digital economy. In official language, this is often called ‘balancing security and development’. For a company, that means you are not told to stop using data. Instead, you are expected to classify your data by risk and to install matching safeguards.
The three tiers of data classification
The starting point for compliance is Article 21 of the DSL, which creates a national data classification-and-grading system. The law itself uses three broad categories.
- General data usually means data that has little impact on national security or public welfare. Typical examples are ordinary marketing documents, internal meeting minutes, or HR records after de-identification.
- Important data is defined in the law as data that, if tampered with, destroyed, leaked, illegally obtained or illegally used, may endanger national security, the public interest, the lawful rights of individuals or the interests of organisations. The wording is intentionally broad so that each industry regulator can specify what counts.
- Core data is the top tier. It concerns national security and could seriously damage the economy, social stability or public wellbeing if compromised. Core data will face the strictest governance, but the law does not list what is included.
For most foreign enterprises, the tier that matters most is important data. That is also where the rules are still evolving.
Who decides what is important?
Under the DSL, the National Data Security Work Coordination Mechanism provides overall coordination, while industry regulators publish catalogues of important data for their sectors. For example, the National Health Commission has issued rules on medical and health data, the Ministry of Industry and Information Technology works on industrial and automotive data, and the People’s Bank of China supervises financial data. Provincial governments also work with regulators to draft local catalogues, so a product can be on a provincial list before it appears on a national one.
Because many catalogues are still being drafted, companies sometimes face ambiguity. The safest way to move forward is to review similar published catalogues in your sector and combine them with any local guidance. When your data clearly resembles a category listed in a published catalogue, treat it as important and begin building the controls and reporting procedures that apply.
What classification looks like inside an automotive supplier
Let’s stay with Sophia at the German-owned plant in Suzhou. When she maps the data flows, she finds four groups: production telemetry and quality-test results stored locally, vehicle maintenance records shared with headquarters in Germany, employee files in the HR system, and a map of supplier locations in the Yangtze River Delta.
Most HR data is covered by the Personal Information Protection Law rather than the DSL’s data-security classification. But the vehicle test data and the supplier map may well be considered important data under the automotive industry catalogues, because leaking them could reveal supply-chain vulnerabilities or sensitive geographic information.
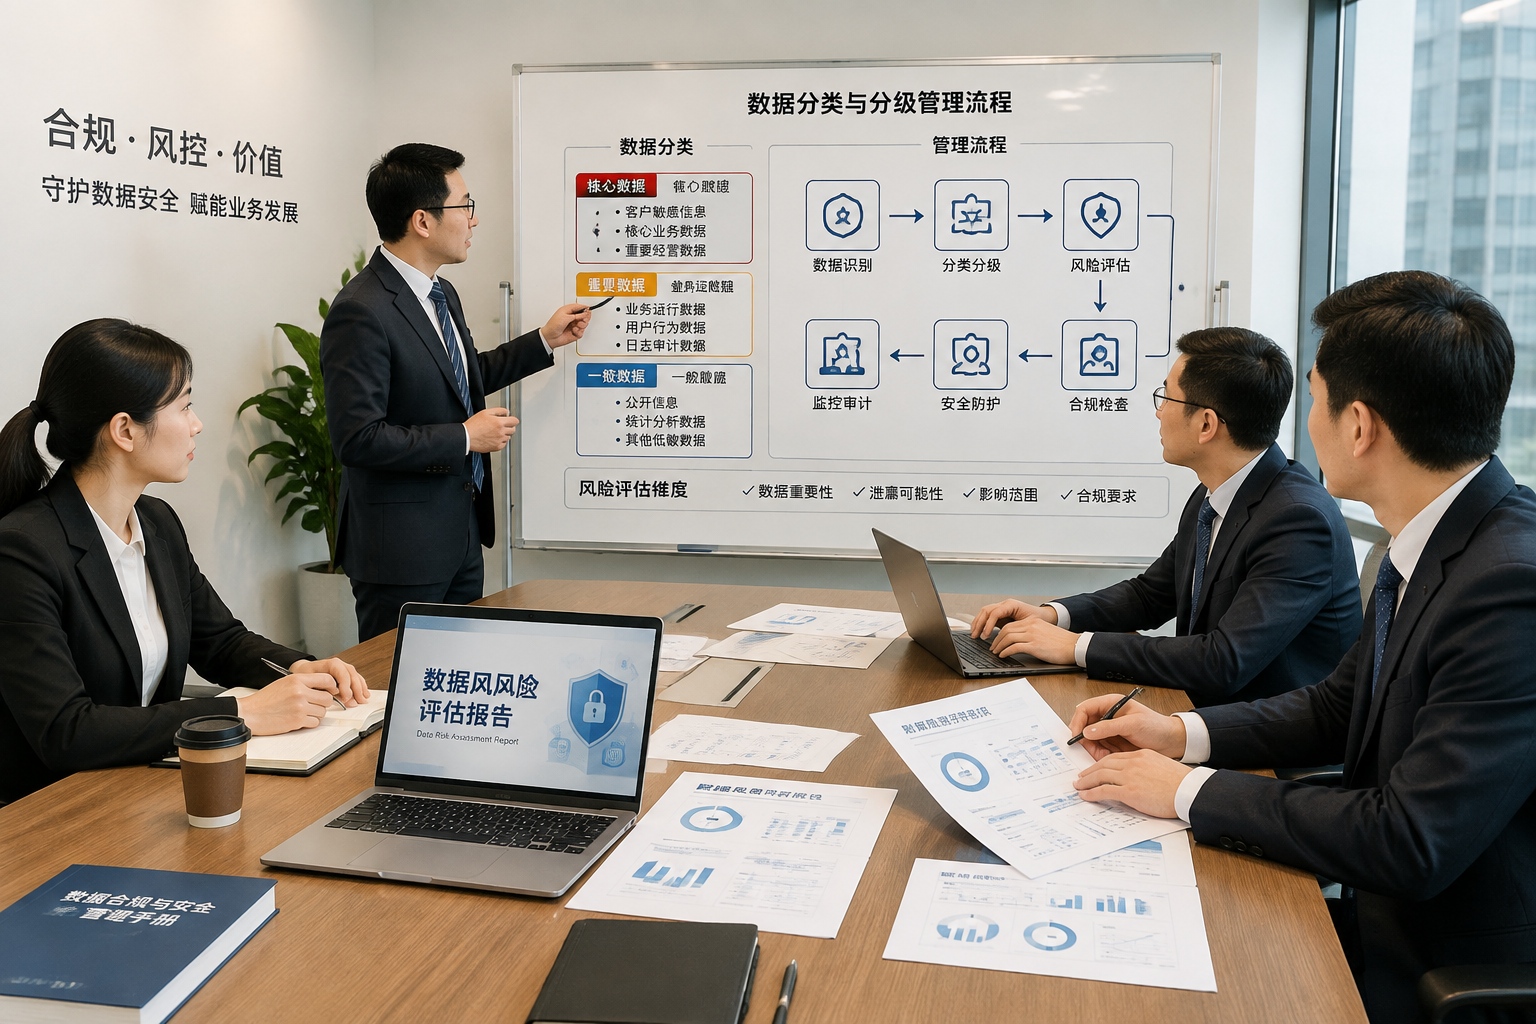
Once a data set is classified as important, extra duties apply. Chapter 4 of the DSL requires the data handler to appoint a data security officer and a dedicated security body, carry out regular risk assessments, and submit a risk assessment report to the relevant regulator. It also says that if important data must be provided to a foreign entity, a security assessment is required first. This is separate from the personal information export rules under the Personal Information Protection Law.
No definitive list? Then document your reasoning
For a company that cannot find a clear answer in a sector catalogue, the reasonable approach is to perform a self-assessment. Use the definitions in the DSL, the classification guides issued by local governments, and hints from earlier drafts of the industry catalogue. Write down how you classified each data type and why. If an authority later disagrees with your conclusion, you can show that the process was responsible and traceable, which often reduces the level of penalty.
Building a compliance plan
Data classification should not become an airtight policy document that sits in a drawer. It has to shape how you run your systems. Here is a four-step approach that works for most foreign-invested entities.
Step 1: know your data. Inventory every database, server, employee device and third-party processor. Describe what data is held, where it lives, who has access, how long it is kept, and whether it can be linked to an individual or to national infrastructure. This inventory will become the core of your compliance file.
Step 2: find the applicable catalogue. Check national industry catalogues, then look at the regulations of the province or city where your data is processed. If no catalogue is available, use the criteria from similar catalogues or a national standard such as Information Security Technology – Data Security Capability Maturity Model.
Step 3: assign a tier and a risk level. For each data type, record whether you believe it is general, important or core. Add a risk rating that takes account of confidentiality, integrity and availability. Timestamp these records so you can prove when the assessment was made.
Step 4: build safeguards. General data needs basic encryption, access control and a backup plan. Important data should have stronger isolation, monitoring, two-person approval and an incident-response plan. Train your staff at least once a year and sign data processing agreements with vendors that touch important data.
If your company decides that it handles important data, the plan needs to go further. You must appoint a data security officer, establish a data security management body, run a risk assessment at least once a year, and send the report to the competent industry regulator. The report should cover the purpose, method and scope of processing, as well as the risk status of the data and the countermeasures already taken. In practice, many regulators do not require a specific form, but an external Chinese law firm can help you draft one that matches local expectations.
What happens if you get the classification wrong?
Penalties depend on the type of violation. If a company fails to fulfil the general data security protection duty in Article 27, which includes failing to establish a classification system, the regulator can order a correction and issue a warning. It may also impose a fine of between RMB 50,000 and RMB 500,000. If the company refuses to correct, or the violation causes serious consequences, the fine ranges from RMB 500,000 to RMB 2 million. Regulators can also suspend related business activities, order a halt to operations, or revoke the business licence in severe cases. The individuals directly responsible, such as the data security officer or the legal representative, may be fined between RMB 10,000 and RMB 200,000 and may be banned from serving in senior positions in the data processing sector for a period.
A mistake can also trigger penalties under the Cybersecurity Law or the Personal Information Protection Law if the same incident involves personal data. In serious cross-border data transfer cases, a non-compliant company could be blocked from sending data abroad, which would disrupt the global operations of a multinational company.
The operational risk is often more painful than the fine. Regulators can inspect your data inventory during a routine security review. If they discover that no classification exercise was ever performed, they may order you to halt data processing until the systems are properly classified. For a factory integrated into a global supply chain, that can mean production delays, delivery penalties and lost trust from overseas headquarters.
Before you start: three practical reminders
First, use the consultation channels that have opened up. Many industry regulators accept written inquiries about whether a specific type of business data falls into the important-data category. Even if the answer is slow, the correspondence itself becomes useful evidence of good faith. Second, watch the pilot programmes. Shanghai’s Lingang free-trade zone, for example, has been testing a more granular list of data that can be transferred abroad. Companies registered there can often make classification decisions based on a clearer set of criteria. Similar pilots are underway in the Hainan Free Trade Port and the Beijing Daxing Airport Economic Zone, so location can materially affect your obligations. Third, do not underestimate the human factor. The law makes data security the responsibility of named individuals. If you are asked to act as the data security officer for a Chinese subsidiary, you should be ready to explain to the board, at least once a year, exactly what is in the company’s important data inventory and how risks are being managed.
Wrapping up
China’s Data Security Law is still young. Sector catalogues are being refined, local rules are changing, and enforcement is becoming more sophisticated. For foreign enterprises, the best approach is to build a classification process that is documented, repeatable and updated regularly. Do not wait for the government to complete every list. Start by mapping your data, assigning tiers, and putting the corresponding controls in place. That will not only keep you on the right side of the regulator, but also give you a clearer picture of the data you hold and why it matters.
Start the discussion at forum.chinacomes.com